
- Partner owns the fallout: Every alert carries the partner brand, so stale or raw alerts become the partner’s support tickets.
- Coverage sets the tiers: Lookups beyond email, such as phone, domain, card, and ID numbers, unlock premium and business plans.
- Freshness beats volume: Source labels and publish dates separate fresh infostealer leaks from recycled compilation data.
- Plans live in the API: Free preview scans, per-user asset caps, and subscription controls keep pricing and backend in sync.
- Privacy by design: Masked output, client-side hashing, and server-side keys keep sensitive values out of screens and logs.
Quick Answer: A white label dark web monitoring API lets a partner run breach and infostealer checks inside its own product. Partners should expect wide identifier coverage, freshness labels, plan-aware user controls, and privacy-safe responses. Event delivery, error handling, and audit evidence then decide whether the feature holds up in production.
A dark web alert carries the partner’s logo, not the provider’s. So when an alert arrives late or repeats old data, the partner absorbs the support ticket. The provider behind the feed never hears about it.
That ticket sits on top of a growing fraud problem. The FTC reported that consumers lost $15.9 billion to fraud in 2025, across 3 million reports. In 2024, by contrast, the total sat just over $12 billion. As a result, users expect their apps to warn them early. They also blame the app that stays silent.
For that reason, a white label dark web monitoring API shapes churn, support load, and renewal value. This guide lists the features CTOs and product leads should expect before they sign. It also explains what each feature changes for a branded product.
Why Missing Features Cost the Partner, Not the Provider
In a white label model, the provider owns the engine and the partner owns the customer. As a result, every gap in the API turns into a gap in the partner’s product. The provider’s contract rarely covers that cost.
Consider an illustrative case with round numbers, not data from any partner. A product monitors 50,000 users. Then a recycled password compilation surfaces, and a weak feed flags 20% of users as newly exposed.
- 10,000 users receive an alert about data that leaked years ago
- If 5% contact support, the team handles 500 tickets in one week
- Each confused user also starts to doubt the next alert
A well-built white label dark web monitoring API prevents most of that week. It labels old data as old, masks sensitive values, and respects each user’s plan.
White Label Dark Web Monitoring API Features at a Glance
The table below groups twelve features partners should expect. Each row ties the feature to its effect on a branded product.
| Feature | What Partners Should Expect | Why It Matters to the Partner |
| Identifier coverage | Email, phone, username, domain, IP, card, bank, and government ID lookups | Plans can grow past email-only checks |
| Source labels | Breach, combolist, or malware, plus finer tags such as infostealer or phished | Support can tell fresh leaks from recycled data |
| Freshness signals | Publish dates and days since last discovery | Alerts say “new” only when the data is new |
| Profile enrichment | Many records merged into one profile per person | Users read one story instead of fifty rows |
| Free preview scan | Aggregate counts without a registered user | Onboarding scans do not consume paid lookups |
| Plan limits | Per-user asset caps the partner sets | Pricing tiers map to limits the API enforces |
| Subscription state | Enable, disable, extend, renew, suspend, and deregister calls | Lapsed users stop consuming paid lookups |
| Event delivery | Batched webhooks with masked values and paged payloads | Alert copy matches the real delivery cadence |
| Removal events | Scan complete, removal confirmed, and data reappeared events | One event model covers the full privacy bundle |
| Redacted output | Masked versions of every personal value | Plaintext passwords never reach a user screen |
| Client-side hashing | Government IDs and card numbers sent as one-way hashes | Raw numbers never leave the partner backend |
| Credentials and errors | Short-lived tokens, one error envelope, and clear retry rules | Engineers can automate recovery safely |
Coverage Features: What a White Label Dark Web Monitoring API Can Look Up
First, coverage decides which plans a partner can sell. An email-only feed supports one basic tier. In contrast, wider coverage supports premium identity tiers and business plans.
Identifier Breadth Beyond Email
A mature API accepts far more than an email address. Partners should expect separate lookups for these identifiers:
- Email address, phone number, and username
- Company domain and IP address
- Payment card and bank account numbers
- National ID, social security, passport, and driver’s license numbers
- Health insurance ID and password exposure
Also, domain lookups deserve special attention from B2B partners. A good API splits domain exposure into employee accounts and consumer accounts. That split lets a partner sell a business tier without building a second product.
Source Labels That Separate Fresh Leaks From Recycled Ones
Raw breach data repeats itself constantly. In June 2025, for example, headlines described 16 billion leaked credentials as a record breach. Analysts soon showed the set mostly held recycled compilation data from older leaks and infostealer logs.
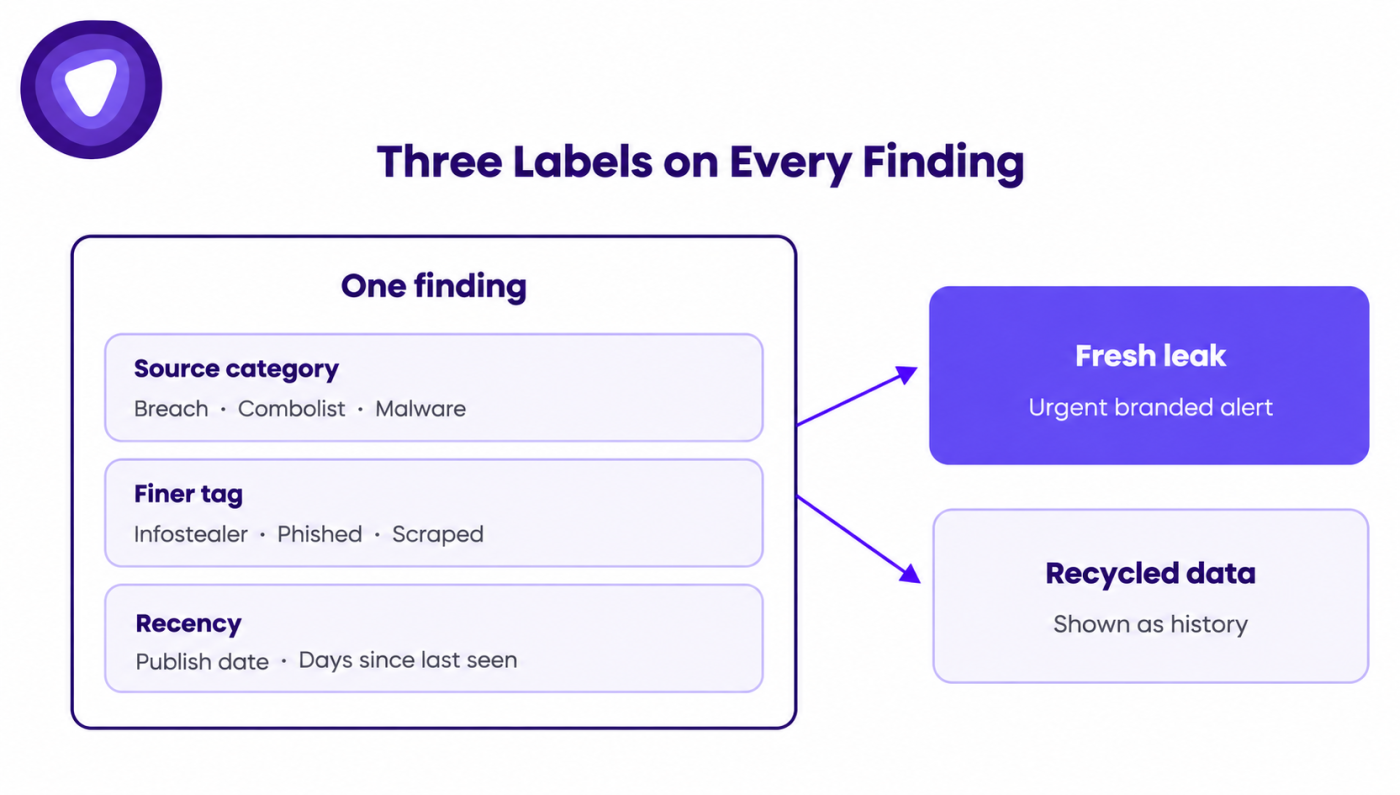
A partner needs labels that expose that difference before an alert goes out. So partners should expect three signals on every finding:
- A main source category, such as breach, combolist, or malware
- A finer tag, such as infostealer, phished, scraped, or exfiltrated
- A publish date plus a count of days since the record last surfaced
With those labels, the product can hold back stale findings or present them as history. Meanwhile, infostealer records with recent dates can trigger the urgent path.
Profile Enrichment Into One View
One email can appear in dozens of breach records. However, showing each row confuses users and inflates support load. Instead, an enrichment endpoint should merge every record into one profile per person. Each field then appears once, with multiple values grouped together.
Product Features: How the API Fits a Branded Plan
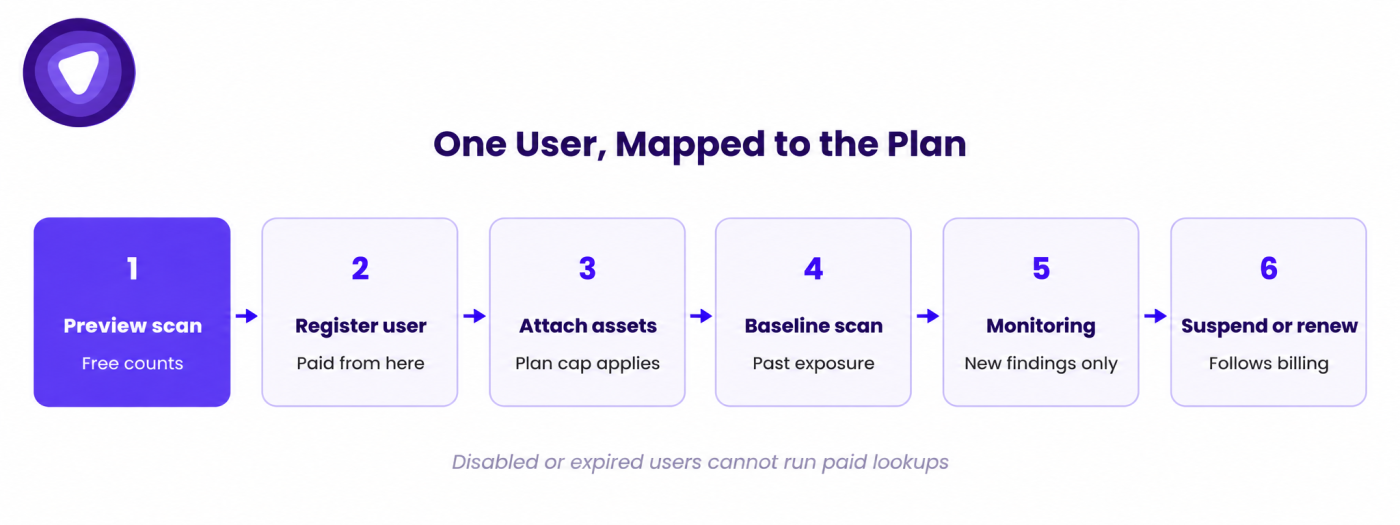
Coverage alone does not make a sellable product. The API also needs controls that match how partners price, bill, and retain users. Four features matter most here.
Free Preview Scans Before Signup
A preview scan shows a prospect their exposure count before they pay. The best APIs separate free aggregate lookups from paid lookups tied to a registered user. A free call returns totals, distinct sources, and recency, but no raw records.
That split protects margin at the top of the funnel. In practice, a partner can run thousands of onboarding scans without paying for users who never convert.
Plan Limits the API Enforces
For example, most partners sell tiers, such as one email on a base plan and five assets on premium. The API should let the partner set a per-user asset cap. When a user exceeds it, the API should reject the request with a clear error.
As a result, the pricing page and the backend stay in sync. Engineers do not need a separate limit system to guard plan boundaries.
Subscription State the API Respects
Next, billing events must reach the monitoring layer. A partner should expect calls to enable, disable, extend, renew, suspend, and deregister each user. Suspension should pause monitoring while keeping history, so a returning user does not lose context.
The API should also refuse paid lookups for disabled or expired users. That rule stops lapsed accounts from running up cost. Some APIs also open renewal only near expiry, which keeps renewal timing tied to billing.
A Baseline Plus Forward Monitoring
Monitoring reports exposure that appears after the partner attaches an asset. It does not, by default, report what leaked before. So a complete onboarding flow runs a full scan at attachment time and stores that baseline.
This two-step model mirrors how an exposure baseline feeds ongoing monitoring. Users see their history once, then receive only new findings afterward.
Delivery Features: How Alerts Reach the Product
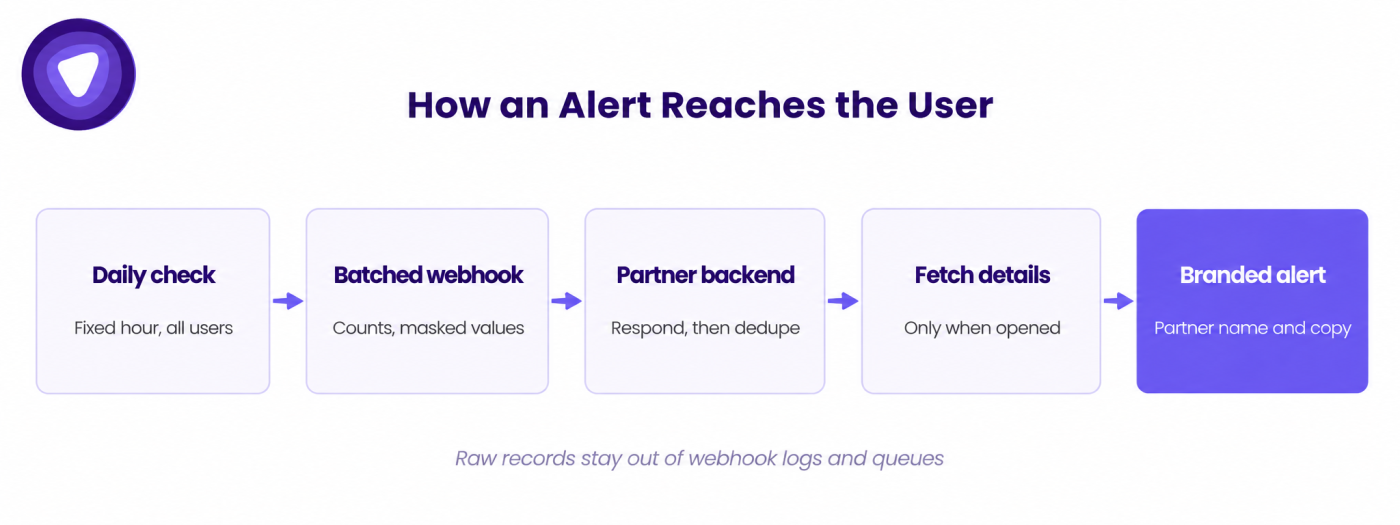
Delivery design shapes the words a partner can promise. A product that says “instant alerts” needs a feed that delivers instantly. A feed that runs on a schedule needs different copy.
Webhooks With a Stated Cadence
First, partners should expect the provider to publish its check cadence. One common model runs a daily freshness check at a fixed hour. It then sends one batched webhook covering every affected user.
A well-designed payload carries counts and partially masked values, not raw records. The partner then fetches details only for users who open the alert. That design keeps sensitive data out of webhook logs and queues.
Duplicates, Ordering, and Paged Deliveries
Webhook handlers also fail in quiet ways. Large batches arrive across several pages, and deliveries can repeat or arrive out of order. Good documentation states this plainly and tells partners to respond first, then process later.
Partners should build idempotent handlers that read every page and ignore unknown event types. Our guide to webhook reliability covers retry and signature testing in more depth.
One Event Model for Monitoring and Removal
Many partners sell dark web monitoring alongside data broker opt-out. In that case, both services should share one event style. Partners should expect removal events for three moments:
- A broker scan finishes
- A broker confirms a removal
- Removed data reappears on a broker site
The last event matters most for retention, because brokers often re-list records. The full removal workflow explains each status behind those events.
Privacy and Security Features Legal Teams Will Check
A monitoring feed moves leaked personal data through the partner’s systems. Therefore, the partner’s legal and security teams will review how that data travels. Four features answer their first questions.
Redacted Responses for Display
Every lookup should offer a redacted variant that masks each personal value. The product can then show users enough to recognize a finding. Meanwhile, the screen never displays a full password or account number.
One-Way Hashing for High-Risk Numbers
Government ID and card number lookups, however, carry the highest risk. A strong API accepts these values only as one-way hashes created on the partner’s side. As a result, the raw number never leaves the partner backend.
Server-Side Keys and Short-Lived Tokens
The partner should hold a secret key on its own servers only. That key buys an access token that expires within an hour. After expiry, a refresh token issues a new one without exposing the secret key again.
Audit Evidence Before the Questionnaire
Enterprise customers will audit the partner’s vendors. So partners should expect SOC 2 Type II and ISO 27001 reports, shared under NDA. Those reports let the partner answer security reviews without delay.
Operational Features Engineers Will Test
Engineers judge an API by how it fails, not how it demos. Several operating details decide whether the integration stays quiet after launch.
- One response envelope: every reply carries a result code and message, so parsing stays uniform.
- Service-specific error codes: the same number can mean different things in each service, and the docs say so.
- Clear retry rules: retry server errors and rate limits with backoff, but fix client errors before resending.
- Account-level rate limits: the account team states the limits, and the client throttles high-volume jobs itself.
- Separate sandbox and production: each environment gets its own base address, kept in configuration.
- Bounded pagination: record lookups return pages of 50, capped at the newest results.
These details read as small. However, each one removes a class of production incident before it reaches a user.
A Feature to Use on Day One: Compromised Password Checks
A white label dark web monitoring API can also harden the partner’s own login flow. NIST SP 800-63B-4 sets the current federal guidance for passwords. It requires verifiers to compare new passwords against a compromised-password blocklist at creation and change.
The same guidance requires a forced password change when evidence shows a credential was compromised. Monitoring alerts supply exactly that evidence. So one integration serves two jobs:
- Screening passwords at signup and reset against known breach data
- Triggering a forced reset when monitoring links a user’s credential to a leak
The revision became final in 2025. So partners that wire it in now answer the password question before a breach forces it.
How to Map These Features to Your Product
Still, features only earn revenue once they surface in the product. Most partners place monitoring at five points in the user journey:
- An onboarding check that shows exposure in seconds
- A premium plan upsell built on continuous monitoring
- A security dashboard with findings and recommended fixes
- Domain monitoring for business customers
- Account takeover alerts tied to recent infostealer findings
For example, SaaS teams often start with the onboarding check and premium upsell. Fintech apps, by comparison, tend to lead with account takeover alerts.
How PureVPN White Label Dark Web Monitoring Delivers These Features
PureVPN White Label Dark Web Monitoring exposes these features through one documented API reference. It covers breach and infostealer data, redacted lookups, hashed ID searches, plan limits, and subscription controls. Real-time monitoring sends batched webhooks with masked values after a daily freshness check.
Partners can also add data broker opt-out across 400+ sites as a separate line. The platform holds SOC 2 Type II and ISO 27001 certification, with audit reports under NDA. The 400+ site and 150+ partner figures are PureVPN’s own reported data, not third-party audited. The platform page shows each deployment path.
Conclusion: Judge a White Label Dark Web Monitoring API by What Users Feel
A white label dark web monitoring API succeeds or fails inside the partner’s product. Coverage, freshness labels, plan controls, honest delivery, and privacy-safe output decide what users actually feel. Each missing feature returns as a support ticket under the partner’s brand.
So the next step is to score each shortlisted provider against the twelve features above. Then plan the rollout with our launch guide, which covers packaging, pricing, and compliance.
Request API sandbox access for a 20-minute integration walkthrough.